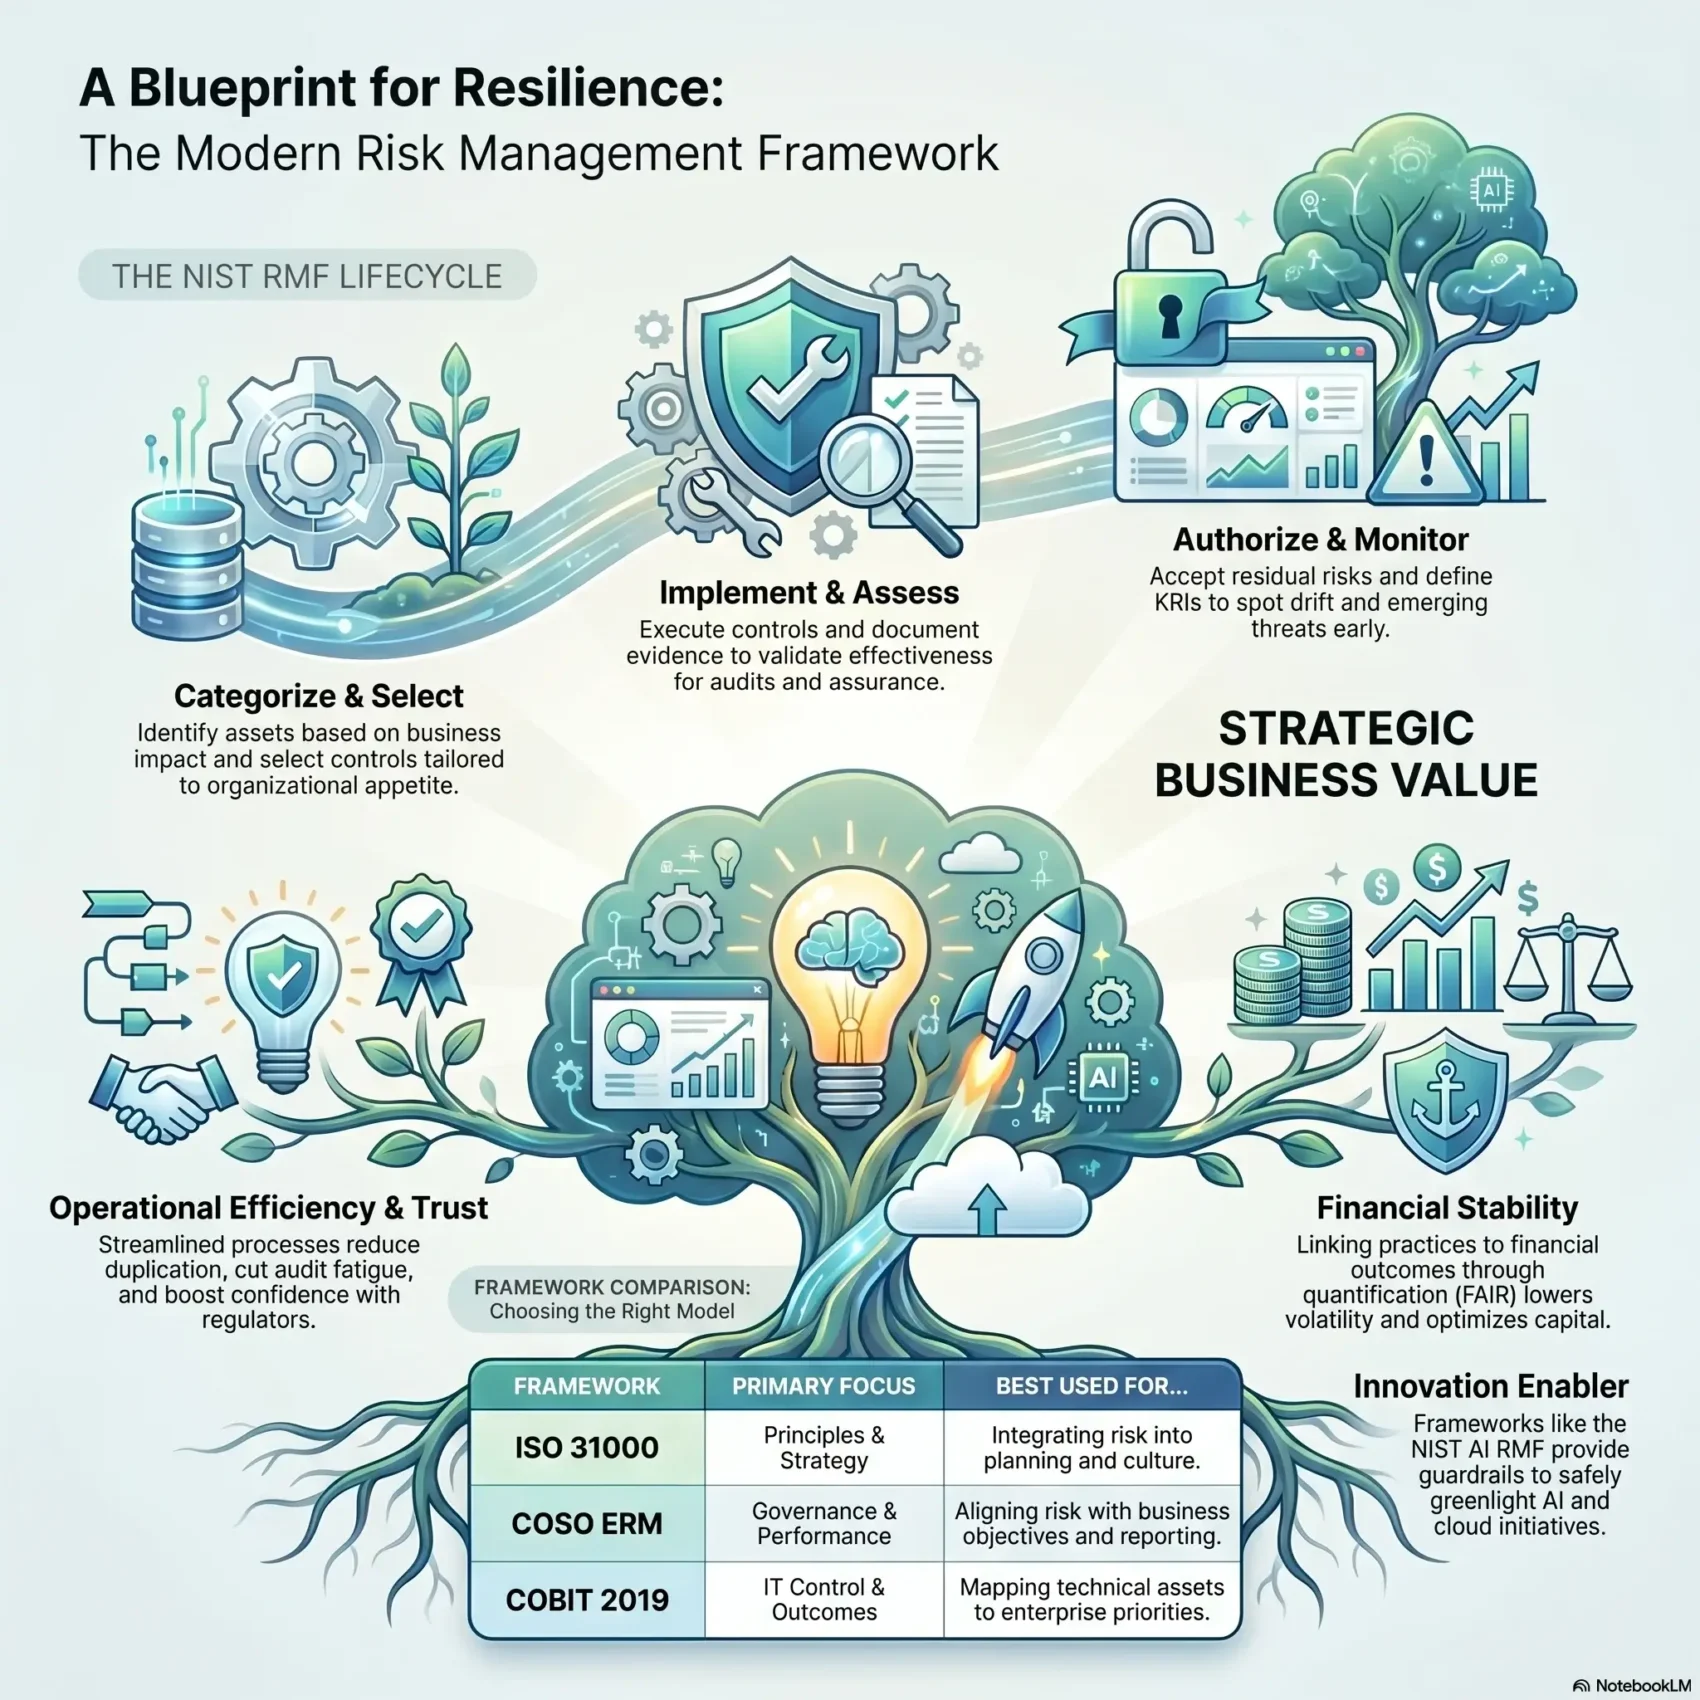
A risk management framework is a written method for spotting what could go wrong in your business, deciding how bad it would be, doing something about it and checking that the fix still works. It replaces scattered opinions with one repeatable process.
Without one, each department judges threats by its own standards. IT worries about ransomware, finance about a late-paying customer, operations about a single supplier, and nobody can say which deserves the next budget euro.
This guide covers what these frameworks contain, which ones are worth knowing in 2026, and how to pick one that fits your company rather than a textbook.
Key Takeaways
- A risk management framework is a repeatable process: identify, assess, treat, monitor, report.
- Enterprise standards (ISO 31000, COSO ERM) set principles; NIST publications and FAIR get specific about security and money.
- Clear owners and escalation paths matter more than the framework you pick.
- Quantifying exposure in currency helps you defend a budget request to finance.
- AI systems now need their own controls, and parts of the EU AI Act already apply.
Why a Risk Management Framework Matters in 2026
Two things changed recently: losses got more expensive, and regulators started asking for written evidence rather than good intentions.
IBM’s 2026 Cost of a Data Breach Report puts the global average cost of a breach at $4.99 million, about 12% higher than the year before. Attacks using AI, such as deepfake impersonation of an executive, added roughly $1 million to the average incident, and more than one in four organizations surveyed had faced one.
Regulators now expect documentation
The EU AI Act is the clearest example. Its bans on unacceptable uses and its AI literacy duty have applied since 2 February 2025, and obligations for general purpose AI models followed on 2 August 2025. From 2 August 2026, Article 50 requires you to tell people when they are dealing with an AI system or AI generated content. Duties for high risk systems listed in Annex III, such as CV screening or credit scoring, were pushed back to 2 December 2027 by the Digital Omnibus agreement, which buys time but removes nothing. Our guide to EU AI Act compliance walks through the obligations by role.
What a consistent approach actually buys you
When every unit scores exposure the same way, you can rank a supplier concentration problem against an unpatched server and fund the bigger one first. You also stop rewriting the same evidence for every audit. For the data foundation underneath this, see our guide to building a data governance strategy.
What a Risk Management Framework Is and How It Works
Think of the framework as the operating manual and the risk register as the live worksheet. The manual says how a threat gets recorded, who owns it, which scoring scale applies, when it is reviewed and who must be told.
The seven pieces most frameworks share
- Identification: naming what could interrupt your objectives, from ransomware to losing your only certified welder.
- Assessment: how likely it is and how much damage it would do.
- Treatment: avoid, reduce, transfer (usually insurance) or accept.
- Monitoring: checking that the chosen control still works.
- Reporting: telling leadership what changed and what needs a decision.
- Governance: who owns what, and who may accept an exposure.
- Improvement: feeding incidents and near misses back in.
From paper to daily work
A framework only earns its keep when it connects to work people already do. The register should live in a tool your teams open anyway, evidence should be collected automatically where possible, and each entry should name a person rather than a department. A control with no name against it is one nobody tests.
Keeping it tied to business objectives
Every entry should trace back to a goal it threatens: revenue, delivery dates, licence to operate, customer trust. If you cannot name the goal, the item belongs in a backlog. Linking data and controls is covered in our guide to data governance and business controls.
The Business Value of Getting This Right
A disciplined process turns uncertainty into decisions you can defend. Three benefits show up consistently.
Fewer surprises. Catching a supplier’s financial trouble in a quarterly review is cheaper than discovering it when a shipment fails to arrive. Our guide to supply chain resilience covers that case.
Less audit fatigue. When evidence is collected as you go, an audit becomes an export rather than a three week scramble. Teams under several overlapping regimes get there faster with the tooling in our RegTech and compliance automation overview.
Faster approvals. A team that can show how a new AI feature will be tested, logged and rolled back gets a yes sooner than one that promises to be careful. The same applies to a cloud migration, where our hybrid cloud strategy guide sets out the guardrails.
Core Components and Steps of an RMF
RMF stands for risk management framework, and in US public sector work it usually means one document: NIST Special Publication 800-37, Revision 2.
The NIST seven step cycle
Revision 2, published in December 2018, added a Prepare step to the original six:
- Prepare: set context, roles and an appetite for exposure before you assess anything.
- Categorize: classify systems and data by the damage a loss would cause.
- Select: choose controls that match the category.
- Implement: put them in place and write down what you did.
- Assess: test whether they work as intended.
- Authorize: a named official accepts the remaining exposure in writing.
- Monitor: watch for drift and repeat.
Outside government, the Authorize step is the one worth copying: it forces someone senior to sign next to an accepted exposure, which changes the conversation.
Scoring: heat maps or money
Most teams start with a qualitative scale, likelihood and impact rated one to five, shown as a heat map. That is fine for triage and hopeless for budgeting, because “high” tells finance nothing. A useful rule: heat map for the whole register, money for the top ten (see FAIR below).
Leading and lagging indicators
A KPI (key performance indicator) tells you how something went. A KRI (key risk indicator) warns you before it goes wrong. Servers missing a critical patch for more than 30 days is a KRI; incidents last quarter is a KPI. Only the first gives you time to act.
Governance, Risk Appetite and Regulatory Compliance
Most frameworks fail on ownership, not method. Three questions settle it: who owns this exposure, who may accept it, and what has to happen before it reaches the board.
Setting an appetite you can actually apply
Risk appetite means how much of a given exposure you will live with in pursuit of a goal. It is only useful written as a threshold somebody can check. “We take security seriously” is not an appetite. “No customer data in a system without multi factor authentication, and any exception expires after 90 days” is one, because it produces a yes or no answer.
Making compliance a by-product
GRC (governance, risk and compliance) works best when one control satisfies several rulebooks. Access reviews serve ISO 27001, SOC 2 and most privacy laws at once. Map controls once and tag them by regime instead of running parallel programs. Our privacy compliance framework guide shows that mapping for data protection rules, and data privacy at work covers employee data.
Leading Enterprise Risk Management Frameworks
Enterprise risk management (ERM) means looking at the whole organization at once rather than one department at a time. Three standards dominate.
ISO 31000:2018: principles first
ISO 31000 is deliberately short and prescribes no controls. It sets principles, a governance structure and a process, and expects you to fold them into decisions you already make. Pick it when you want something adaptable and are prepared to fill in the detail. It is guidance rather than a certifiable standard, so there is no ISO 31000 certificate.
COSO ERM: governance tied to performance
COSO is a US private sector body whose 2017 ERM framework organizes the subject into five components and twenty principles, linking culture and governance to strategy, performance and reporting. It speaks the language boards and auditors already use, which suits listed companies and regulated finance.
COBIT 2019: translating IT into business terms
COBIT, from the professional association ISACA, is built for the gap between technology controls and business objectives. If the board cannot tell whether IT spending reduces exposure or simply grows, COBIT gives you that mapping.
Cybersecurity Frameworks Worth Knowing
NIST Cybersecurity Framework 2.0
CSF 2.0, published in February 2024, describes outcomes rather than mandatory controls. It added a sixth function, Govern, alongside Identify, Protect, Detect, Respond and Recover, putting accountability and strategy on the same footing as technical defence, and widened the scope beyond critical infrastructure to organizations of any size. Its Quick Start Guides are a reasonable first week of work. See also our overview of current cybersecurity trends and our cybersecurity mesh guide.
FAIR: putting a number on it
FAIR stands for Factor Analysis of Information Risk. Instead of calling something “high”, it estimates how often a loss event is likely to happen and how much it would cost, then expresses the result as a range in currency. That is what lets you say a control costing $200,000 addresses an exposure estimated between $1 million and $4 million a year. Use it for the handful of decisions where the number changes the answer, not for every line of the register.
OCTAVE and TARA
OCTAVE starts from your assets: decide which data and systems the business cannot lose, then look for weaknesses around them. TARA, developed at MITRE, starts from the attacker, using libraries of known threat agents and methods. Asset first suits stable environments; threat first suits teams facing a specific adversary.
Preparing for the encryption change
One long term item belongs on every register now: data stolen today can be decrypted later once quantum computers mature. Our guide to quantum-safe encryption covers the standards and deadlines.
AI Risk Management Frameworks and Standards
AI needs separate treatment because the failure modes differ. A model does not crash; it quietly gives a worse answer for one group of applicants than another.
NIST AI Risk Management Framework 1.0
Released in January 2023 and voluntary, the AI RMF organizes the work into four functions: Govern, Map, Measure and Manage. A companion Playbook offers concrete suggestions for each, and NIST publishes crosswalks to other standards, which saves rebuilding a control set from scratch.
The Generative AI Profile
NIST-AI-600-1, published in July 2024, lists twelve risks specific to generative AI, including confabulation (confidently wrong output), data leaking through prompts and harmful bias, with suggested actions for each. It is the practical starting point if your exposure comes from staff using chat tools rather than models you build. Pair it with written generative AI usage guidelines so employees know what may go into a prompt.
ISO/IEC 42001:2023
This is the first certifiable management system standard for AI. It works like ISO 27001 does for information security: you define policies, assign responsibilities, document model testing and run internal audits, and a certification body assesses the result. Enterprise buyers increasingly ask for that certificate rather than a promise.
Where AI risk meets employment law
Hiring is the area most likely to catch an ordinary company. Automated screening counts as high risk under EU rules and is already regulated in several US states. Our guides to AI hiring bias and algorithmic management cover what is required, AI employee monitoring covers surveillance, and explainable AI covers the documentation contestable decisions need. For the layer above all of these, see our AI governance model.
How to Choose and Implement a Risk Management Framework
Start with fit, not popularity
Four questions narrow the field. Which rules already bind you? Who asks you for evidence: auditors, enterprise customers, a regulator? How mature is your process, honestly? How much appetite does leadership have? A twelve person company adopting full COSO ERM produces paperwork nobody reads.
Crosswalk instead of restarting
If you already run ISO 27001 controls, do not rebuild them for CSF 2.0. Use the published crosswalks to map what you have to the new outcomes and work only on the gaps.
A realistic first ninety days
- Weeks 1 to 3: agree scope, write appetite thresholds, name owners for the top ten exposures.
- Weeks 4 to 8: build one register, map existing controls to your framework, mark the gaps.
- Weeks 9 to 12: close two or three gaps, automate one piece of evidence collection, run the first review.
Automating evidence collection early keeps the program alive, because manual screenshot gathering is the step teams quietly abandon. The same discipline applies to choosing what to automate, covered in our guide to automation risk assessment.
Measuring whether it works
Track four numbers: how many top exposures have a named owner, how long remediation takes against target, how many controls failed their last test, and how often a review changed a decision. The last one is the honest test. Structured methods, covered in our guide to decision-making models, help turn the review into a choice rather than a status update.
Conclusion
These frameworks are not competitors. Most companies end up with a blend: ISO 31000 or COSO ERM for the overall shape, CSF 2.0 for security outcomes, FAIR where a number changes the answer, and the NIST AI RMF or ISO/IEC 42001 as AI reaches daily operations.
What separates a working program from a binder is unglamorous: named owners, thresholds that give a clear answer, automatic evidence collection, and a review meeting that occasionally changes what the company does. Start with the ten exposures that would genuinely hurt. For help linking data and controls, see our guide to data governance and business controls.
Found this useful?
Make SmartKeys a preferred source on Google, and our articles will surface more often in your Top Stories, AI Overviews, and AI Mode.
Add as Preferred Source